HOL Guard
Local-first runtime firewall that intercepts AI coding agent tool calls before they run
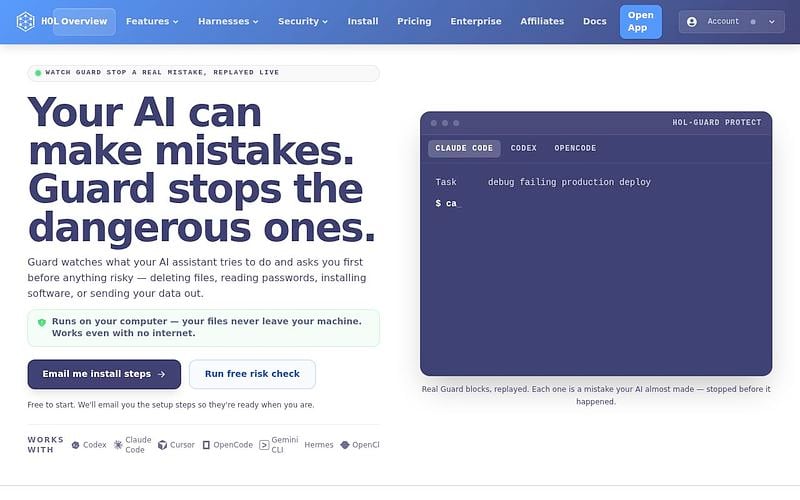
HOL Guard sits between an AI coding agent and the machine it runs on, checking each tool call before it executes. Shell commands, file reads, package installs and MCP server calls are evaluated against policy, then blocked or held for approval.
The stated targets are secret and credential exposure, destructive file operations, prompt injection and malicious packages. Everything runs locally, so prompts and files are not sent anywhere, and it works offline.
Supported harnesses include Claude Code, Codex, Cursor, OpenCode, Gemini CLI and OpenClaw. The Guard Local runtime is open source under Apache-2.0; the hosted app and enterprise features are separate.
HOL Guard Alternatives
Explore 54 products in the Observability & Analytics category. View all HOL Guard alternatives.

Guardrails AI
Open-source framework for adding input and output validators around LLM calls


NeMo Guardrails
NVIDIA toolkit for adding programmable guardrails to LLM conversational apps
AI Gateway HQ
LLM gateway built around spend limits enforced before a request reaches a provider
AISIX
Open-source AI gateway in Rust with one OpenAI-compatible API across 100+ LLM providers
2kw.ai
EU-hosted AI integration platform combining a provider gateway, document extraction, evals and cost observability
Work on HOL Guard? Feature it at the top of Observability & Analytics.
Is your product missing?